Running your own VPN gives you absolute power over your network privacy, data routing, and internal network security. While commercial providers force you to trust third-party servers, building a self-hosted VPN guarantees that your encrypted tunnel remains strictly within your control.
To deploy your private network instantly, register here to provision your cloud infrastructure on TezHost in minutes.
Reasons to Run Your Own VPN on a VPS
Taking total ownership of your encrypted network traffic delivers remarkable technical and financial advantages:
- Absolute Privacy & Zero Data Logging: Commercial providers can secretly track your traffic; running your own VPN ensures no third party logs your online activity or DNS queries.
- Dedicated, Unshared IP Addresses: Unlike commercial VPNs where thousands share an IP (causing CAPTCHAs and sudden IP bans), a self-hosted own VPN provides a clean, dedicated public IP.
- Full Speed & Zero Bandwidth Throttling: Commercial providers throttle speeds during peak hours; your own VPN on high-speed hardware utilizes your server’s full network port.
- Secure Access to Private Infrastructure: Route encrypted traffic straight to internal databases, staging servers, and IoT networks without exposing ports to the public web.
- No Monthly Per-Seat Client Subscriptions: Scale your connection to dozens of client phones, laptops, and remote workers without paying per-user software licenses.
- Bypass Aggressive Regional Censorship: Traditional commercial VPN protocols get blocked easily; running WireGuard on custom UDP ports makes your own VPN traffic difficult to detect.
- Complete Infrastructure Ownership & Custom Routing: You control firewall rules, Split-Tunneling settings, custom DNS resolvers (like Pi-hole), and administrative access.
If you need help selecting hardware specs for your network load, talk to a sales agent right now for a personalized deployment recommendation.
What Is a Self-Hosted VPN?
A self-hosted VPN is a private encrypted server that you independently manage and operate on isolated virtual infrastructure. Instead of routing your data through crowded commercial servers, a self-hosted setup routes your traffic straight through your designated endpoint.
Your Phone / Laptop
       ↓
Encrypted WireGuard Tunnel
       ↓
Your Private VPS
       ↓
Target Internet Site / Internal Network
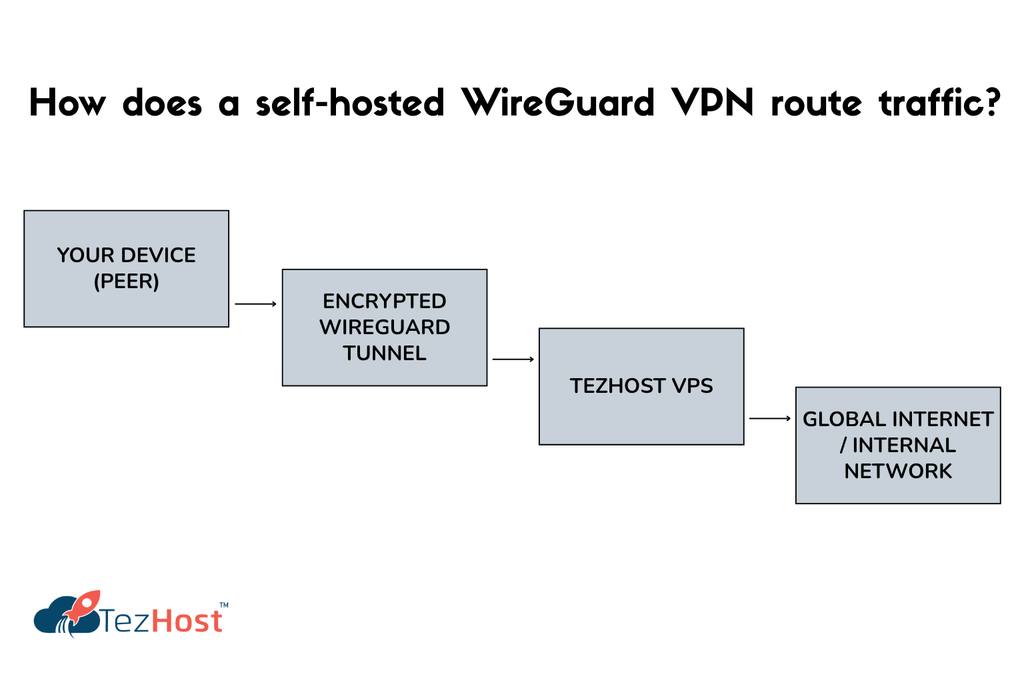
By setting up your own VPN, you become the sole administrator capable of managing client keys, firewall rules, and internal access policies.
To launch a high-performance network endpoint immediately, browse our robust cloud servers built for high-density network throughput.
What Is WireGuard?
WireGuard is an extremely fast, state-of-the-art VPN protocol designed to replace bulky legacy protocols like OpenVPN and IPsec. Running your own VPN on WireGuard gives you access to modern cryptography (Curve25519 and ChaCha20-Poly1305) packed into a lightweight codebase.
It establishes instant connections, handles network switching (like switching from Wi-Fi to cellular) without dropping, and runs natively across Linux, Windows, macOS, Android, and iOS.
Why Combine WireGuard with a VPS?
Combining WireGuard with a virtual private server provides the ultimate balance of modern software and dedicated hardware:
- WireGuard provides: High-speed encryption, peer-based public-key authentication, low CPU overhead, and cross-platform clients.
- A VPS provides: A persistent public IP address, 99.9% network uptime, configurable CPU/RAM, and total root access.
Together, they allow you to run your own VPN endpoint that is accessible from anywhere in the world 24/7.
For high-speed server deployments, explore our isolated VPS hosting packages featuring generous 20TB monthly bandwidth allocations.
How Does a WireGuard VPS Work?
When you connect to your own VPN, your device initiates a lightweight cryptographic handshake with your server.
[ Local Client Device ]
          |
   (UDP Encrypted Tunnel)
          v
[ WireGuard VPS Endpoint ]
     /          \
    v            v
(Public Web)   (Private Server Network)
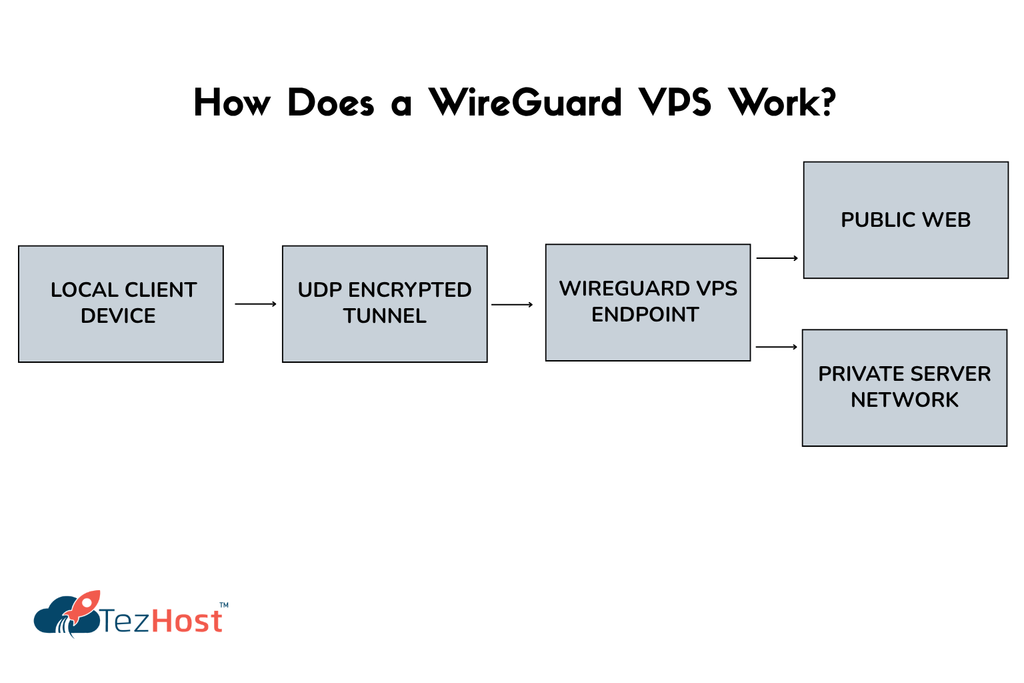
Depending on your routing choices, your own VPN can operate in two primary modes:
- Full Tunnel: Encrypts 100% of your internet browsing traffic through your server’s public IP.
- Split Tunnel: Directs only traffic meant for private office servers through the VPN while keeping standard web traffic on your local connection.
What Do You Need to Run Your Own VPN?
To establish a fully functional own VPN environment, you only need four core components:
- A Reliable VPS: A cloud instance running an operating system like Ubuntu or Debian with a dedicated IPv4 address.
- WireGuard Server Engine: The underlying networking software configured with public/private keypairs, NAT forwarding, and firewall rules.
- Cross-Platform VPN Clients: The official WireGuard app installed on your phone, laptop, or desktop computer.
- Network Access Policies: Your custom routing rules defining whether client traffic accesses the public web or private cloud subnets.
If you are unsure which Linux distribution fits your stack, talk to a sales agent to get expert setup guidance.
How WireGuard Authentication Works
WireGuard uses public-key cryptography—similar to SSH—to establish identity and secure peer connections:
- Private Key: Stored strictly on the local device; never shared across the network.
- Public Key: Shared between the server and the client to verify authorized peers.
When establishing a connection for your own VPN, the server verifies the incoming public key against its authorized configuration file, granting instant access without tedious username/password prompts.
Can You Run a VPN Without a Commercial Provider?
Yes, absolutely. By running your own VPN on a private server, you eliminate monthly commercial provider fees entirely. However, operating a self-hosted endpoint means taking personal responsibility for server maintenance:
- Applying regular Linux system updates.
- Securing administrative SSH keys.
- Managing authorized client configuration profiles.
- Monitoring firewall configurations and resource usage.
WireGuard vs. Commercial VPNs
| Feature | Commercial VPN | Self-Hosted Own VPN |
| Server Control | Managed by third party | 100% Controlled by you |
| IP Address | Shared with thousands | Dedicated private IPv4 |
| Data Privacy | Subject to provider policy | Complete data sovereignty |
| Logging | Provider promises “No Logs” | Hardware-level verification |
| Custom Subnets | Impossible | Fully customizable routing |
| Maintenance | Handled by provider | Self-managed / One-Click |
How TezHost is Revolutionizing the Field
TezHost is revolutionizing the field by converting complex cloud networking and Linux terminal management into an effortless, accessible one-click experience. Building your own VPN historically required hours of manual terminal work—generating cryptographic keys, configuring iptables forwarding rules, and troubleshooting broken NAT configs.
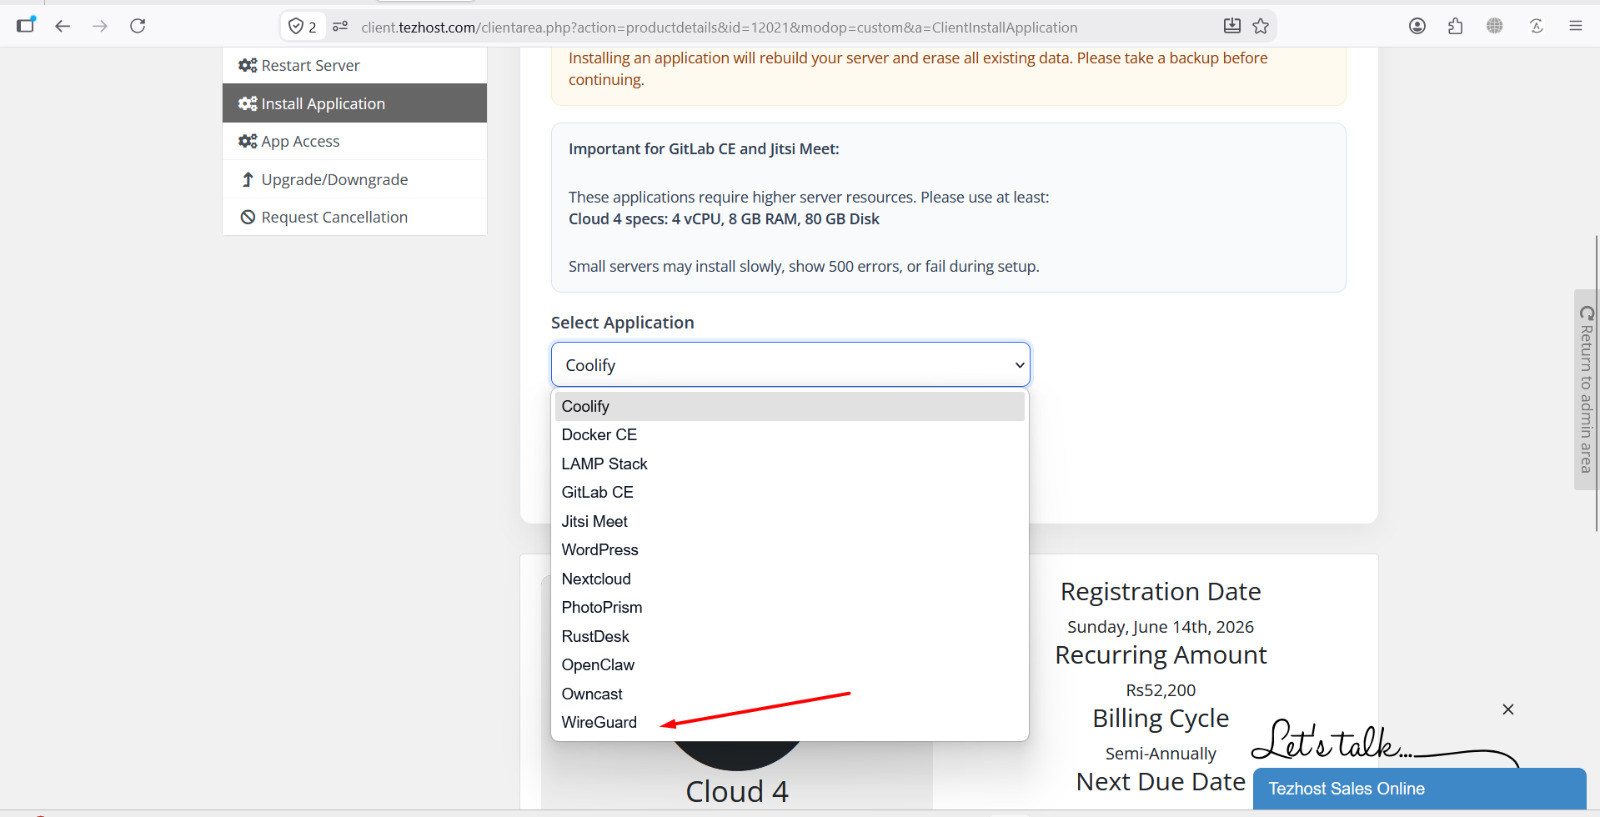
- Automated One-Click WireGuard Deployment: TezHost is revolutionizing the industry with pre-configured software templates that deploy production-ready WireGuard environments automatically upon server provisioning.
- Enterprise Infrastructure & Massive Bandwidth: We pair this software automation with unthrottled server specs, full root access, and a massive 20TB monthly bandwidth allocation on every plan.
- Ecosystem Compatibility: Whether you need private networking for managed hosting for WordPress, database clusters, or dedicated hardware, our high-speed network integrates seamlessly with dedicated server infrastructure.
To discover how our automated cloud deployment simplifies your workflow, talk to a sales agent today.
Choose the Right VPS for Your Own VPN
Choose the right VPS. Selecting the right hardware for your own VPN depends on your active user count and network throughput needs:
- Cloud 2: 2 vCPU | 4 GB RAM | 40 GB SSD | 20 TB Bandwidth ($17/mo) — Perfect for personal use & mobile devices
- Cloud 4 (Recommended): 4 vCPU | 8 GB RAM | 80 GB SSD | 20 TB Bandwidth ($30/mo) — Ideal for small businesses & remote dev teams
- Cloud 6: 8 vCPU | 16 GB RAM | 160 GB SSD | 20 TB Bandwidth ($70/mo) — Built for agency subnets & heavy office traffic
- Cloud 8: 16 vCPU | 32 GB RAM | 320 GB SSD | 20 TB Bandwidth ($130/mo) — Enterprise-grade power for high-density corporate tunnels
Every plan includes dedicated IPv4, free data migration, full root access, and zero traffic throttling. Protect your public domain connections further by securing your web endpoints with our SSL certificates.
Common Mistakes to Avoid When Hosting Your Own VPN
When managing your own VPN, avoid these critical configuration mistakes:
- Exposing SSH Ports Unprotected: Always use SSH keys instead of passwords to secure administrative access.
- Misconfiguring AllowedIPs: In WireGuard client configs, setting
AllowedIPs = 0.0.0.0/0routes all traffic through the VPN, whereas setting a specific IP (e.g.,10.0.0.0/24) enables Split-Tunneling. - Ignoring OS System Updates: Regularly run system updates on your server to patch underlying security vulnerabilities.
- Leaking Private Keys: Never share a client’s private key; generate a unique keypair for every device connected to your own VPN.
Frequently Asked Questions
Can I really run my own VPN?
Yes. You can run your own VPN by installing WireGuard on a private cloud server, granting you total authority over encryption and traffic logs.
Is WireGuard better than OpenVPN for a self-hosted VPN?
WireGuard is significantly faster, lighter, and consumes less CPU power than OpenVPN while offering modern cryptographic security.
Can I use my own VPN on Android and iPhone?
Yes. Official WireGuard applications are available on iOS and Android, allowing mobile devices to connect to your own VPN via a QR code scan.
Do I get a dedicated IP address with my own VPN?
Yes. When you host your own VPN on a virtual private server, you receive an isolated, static public IP address.
Conclusion: Take Control of Your Private Network Today
Building your own VPN with WireGuard and cloud server infrastructure is the ultimate strategy for achieving true online privacy, dedicated network speeds, and secure remote infrastructure access. By replacing commercial subscriptions with a self-hosted server, you retain total data sovereignty and unthrottled performance.
With TezHost, setting up a server takes just a few clicks. Don’t compromise your privacy on shared commercial networks. Talk to a sales agent today, deploy your private cloud instance on our high-speed cloud servers, and take complete control of your digital security!