Learning how to build your own VPN with WireGuard on a high-performance VPS gives you complete freedom over your digital privacy, network routing, and data security. If you want to bypass strict per-user subscription fees, avoid rate-limited public VPNs, and enjoy absolute network peace of mind, self-hosting is the ultimate choice.
To launch your private VPN server in minutes, register here to deploy your environment using TezHost’s automated cloud infrastructure. If you need tailored advice on selecting optimal server resources, talk to a sales agent today.
What Is a Self-Hosted VPN?
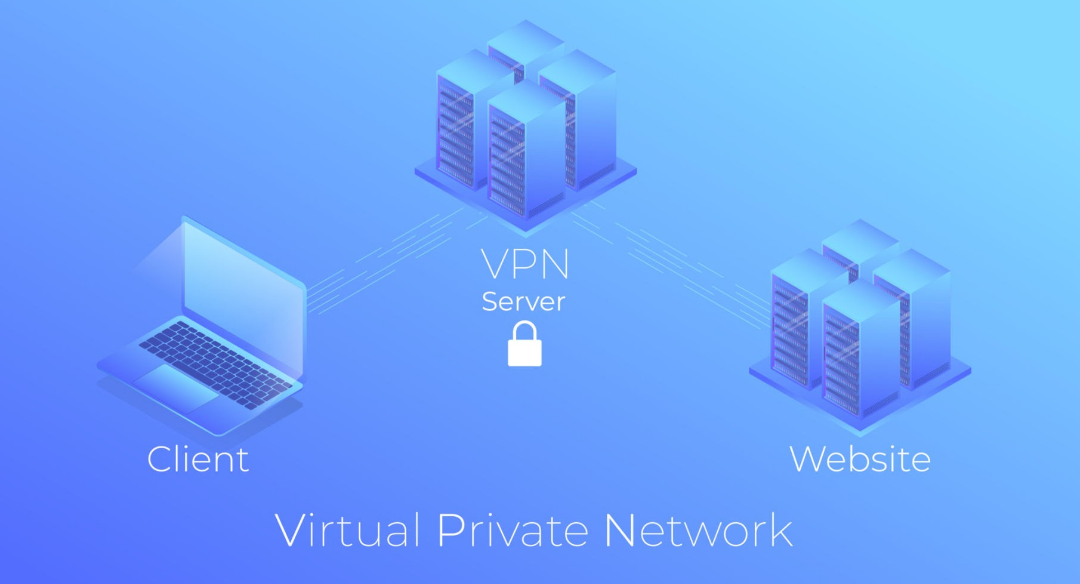
A self-hosted VPN is an encrypted network gateway that you operate on your own dedicated cloud instance rather than routing traffic through a commercial VPN provider.
How does a self-hosted WireGuard VPN route traffic?
It routes traffic directly through a private point-to-point tunnel between your device and your cloud server.
Your Device (Peer) ───[ Encrypted WireGuard Tunnel ]───> TezHost VPS ───> Global Internet / Internal Network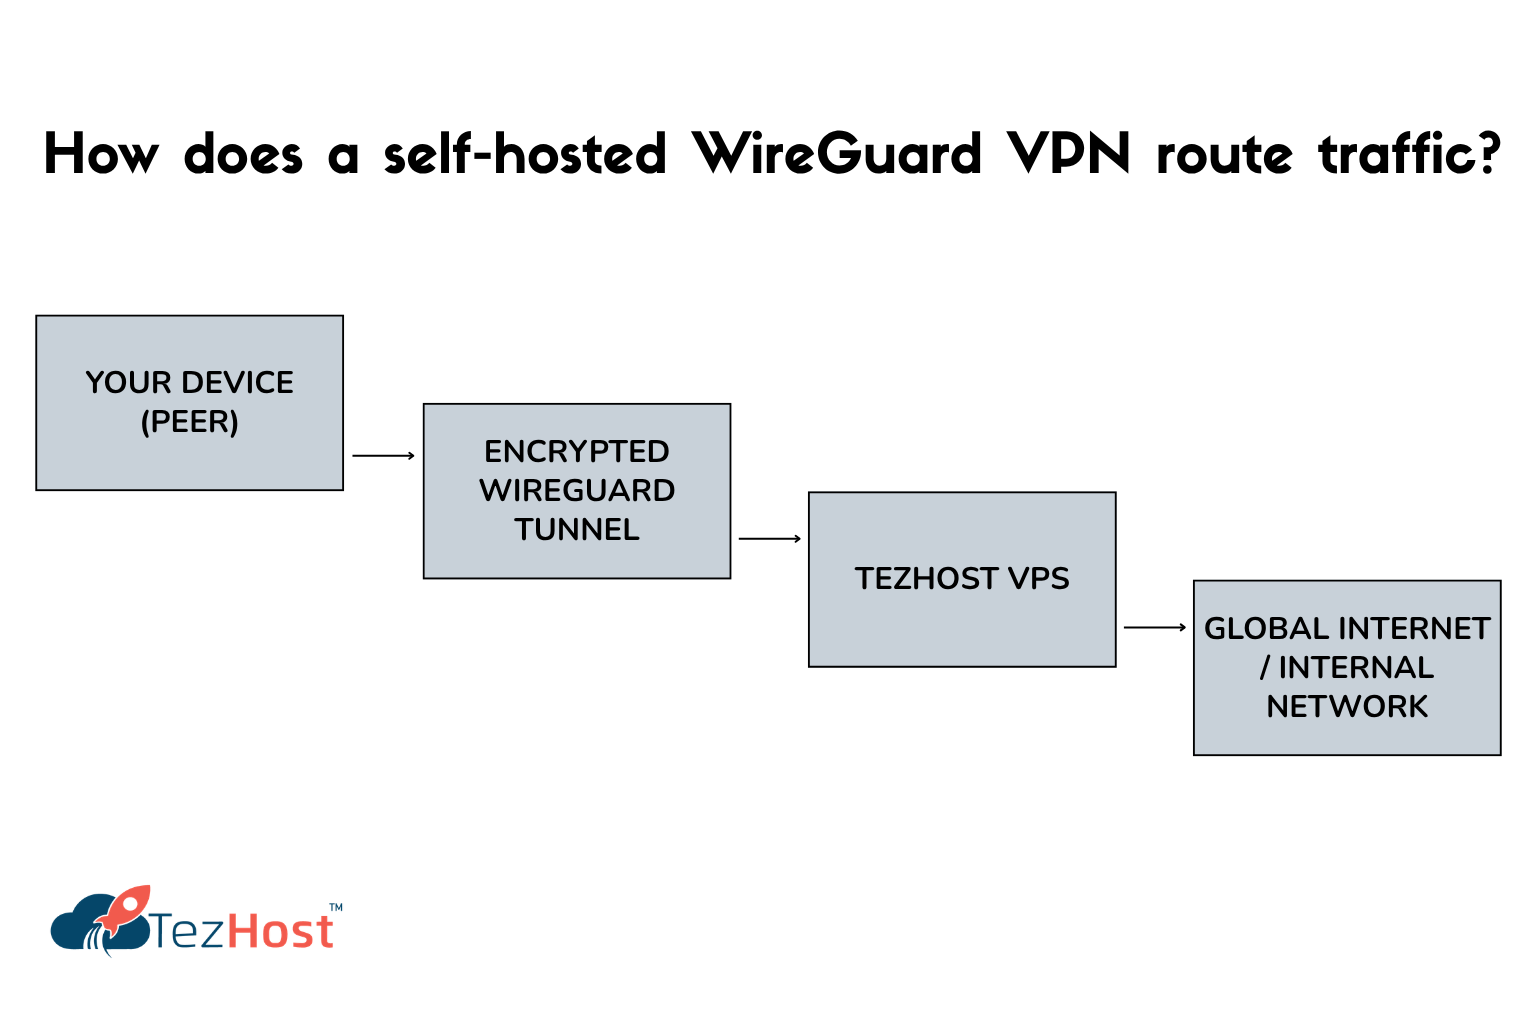
By mastering how to build your own VPN, you retain total sovereignty over:
- Server & Firewall Rules: Full root control over system packages, ports, and access rules.
- Peer Management: Complete authority over active client profiles and crypto keys.
- Network Throughput: Uncapped speed unthrottled by commercial middleman networks.
- Data Privacy: Guaranteed zero-log policies operating strictly within your private network boundary.
Why Use WireGuard to Build Your Own VPN?
WireGuard operates directly within the Linux kernel, utilizing modern cryptographic primitives like ChaCha20, Poly1305, and Curve25519 to deliver state-of-the-art security with minimal CPU overhead.
Why is WireGuard better than legacy protocols like OpenVPN?
WireGuard features an extremely lightweight codebase (~4,000 lines of code), offering significantly faster connection times, lower latency, and superior battery efficiency on mobile devices.
To run a reliable WireGuard network, explore TezHost’s high-speed VPS hosting packages optimized for continuous high-bandwidth performance.
What Do You Need to Build Your Own VPN?
Setting up a private, high-performance VPN requires four foundational components:
- A Reliable VPS: A Virtual Private Server featuring a dedicated public IP address, kernel support, and full root access.
- WireGuard Software: The core engine installed on both the server (listening peer) and client devices (connecting peers).
- Client Applications: Official WireGuard mobile or desktop clients for Windows, macOS, Linux, iOS, or Android.
- Network & Firewall Routing: Properly configured IP forwarding, IP tables, and UDP port rules (default:
51820).
7 Proven Steps to Build Your Own VPN with WireGuard
Executing a manual deployment requires navigating SSH consoles, compiling dependencies, generating key pairs, and establishing complex NAT configurations. However, taking a structured approach ensures seamless connectivity.
1.Select Your Cloud VPS Infrastructure:Secure dedicated performance for your encrypted network.
Choose a cloud server with reliable network throughput and low latency. For high-capacity multi-user setups, review our enterprise-grade cloud servers.
2.Install WireGuard Packages:Skip terminal commands via automated tooling.
Install the core software on your operating system. If you want to bypass command-line overhead completely, use TezHost’s One-Click WireGuard Installation to auto-configure Docker containers, firewalls, and network interfaces in seconds.
3.Generate Public and Private Key Pairs:Establish cryptographic peer authentication.
Generate asymmetric key pairs for both server and client devices. Private keys remain protected on the host device, while public keys are exchanged to establish trusted handshakes.
4.Configure the Server Interface:Set up listening ports and subnet parameters.
Define the server’s private VPN subnet (e.g., 10.0.0.1/24), set the listening UDP port (51820), and assign peer public keys inside wg0.conf.
5.Enable IP Forwarding and NAT Configuration:Route traffic beyond the VPN tunnel.
Enable IPv4/IPv6 packet forwarding inside /etc/sysctl.conf and configure iptables rules to masquerade outbound traffic through the primary network interface.
6.Generate Client Configuration Files:Prepare profiles or QR codes for easy connection.
Build device-specific .conf profiles detailing the client’s private key, assigned VPN IP, DNS servers, and the endpoint IP of your VPS.
7.Activate the Tunnel and Test Connection:Handshake verification and leak checking.
Start the interface (wg-quick up wg0) and import configuration files onto your mobile or desktop devices. Verify active handshakes and test for DNS/IP leaks.
How TezHost Is Revolutionizing the Field
TezHost is revolutionizing the field by transforming complex network engineering into accessible, one-click automated cloud deployments. Building an enterprise-grade VPN server used to demand hours of manual Linux system administration, firewall tweaking, and routing setup.
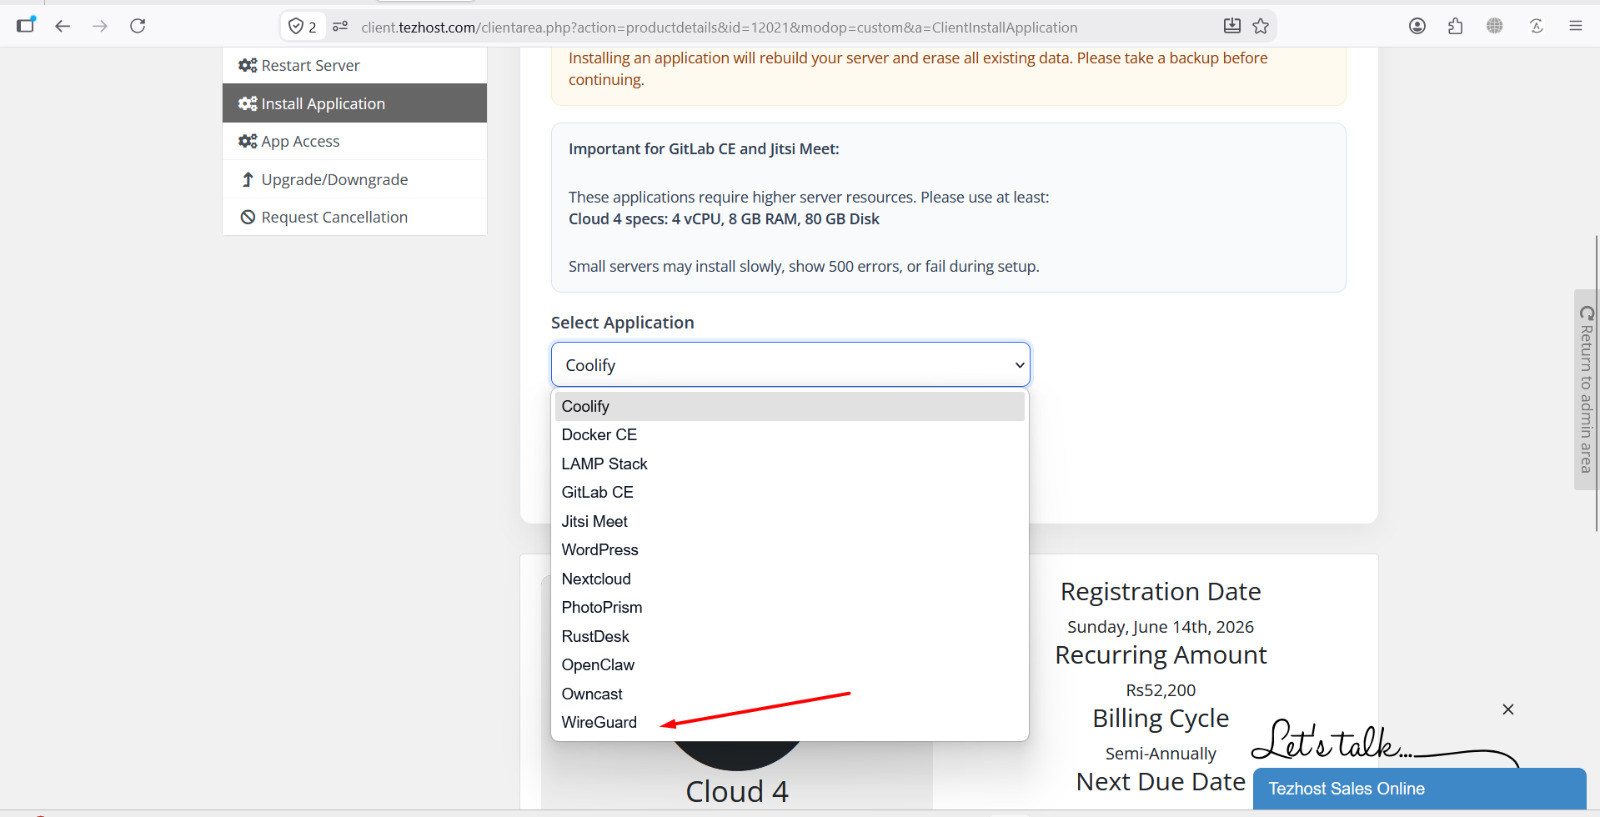
TezHost eliminates technical friction by offering:
- Instant One-Click Deployments: Automated installers that deploy fully configured WireGuard environments alongside containerized management stacks.
- Complete Infrastructure Flexibility: Seamlessly scale your network from flexible virtual nodes to ultra-robust dedicated servers.
- Comprehensive Web Ecosystem: Combine your private VPN with automated platforms like WordPress managed hosting or secure web endpoints protected by enterprise SSL certificates.
If you want to experience this revolutionary approach to cloud infrastructure, talk to a sales agent right now.
Self-Hosted WireGuard VPN vs. Commercial VPN Services
Is a self-hosted WireGuard VPN better than a commercial subscription?
Yes, for users prioritizing speed, dedicated IPs, full system control, and no shared bandwidth throttling.
| Feature | Commercial VPN Service | Self-Hosted WireGuard VPS |
| Infrastructure Control | Third-party managed | 100% You maintain full root access |
| Pricing Model | Recurring monthly per-seat fee | Fixed server price (unlimited client devices) |
| Bandwidth & Speed | Frequently throttled during peak hours | Uncapped high-speed port connectivity |
| Dedicated IP | Expensive add-on or shared | Included with your VPS instance |
| Custom Network Architecture | Locked down | Completely customizable subnets & routing |
What Can You Do with Your Own Private VPN?
Understanding how to build your own VPN opens up powerful capabilities across personal and enterprise workflows:
- Secure Remote Team Access: Connect distributed employees directly to internal staging environments and corporate databases without exposing ports to the public internet.
- Site-to-Site Cloud Interconnects: Link remote office servers directly to cloud infrastructure via persistent background tunnels.
- Private Mobile Browsing: Secure mobile traffic on untrusted public Wi-Fi networks using lightning-fast WireGuard handshakes.
- Access Control for Administrative Dashboards: Lock down server management tools (cPanel, SSH, database consoles) so they are only reachable when connected to your private VPN.
Frequently Asked Questions
Is building your own WireGuard VPN difficult?
While manual Linux terminal configuration requires technical knowledge, using TezHost’s One-Click WireGuard Installation allows anyone to deploy an operational server in minutes without command-line complexity.
Can I run a WireGuard VPN on a small VPS?
Yes. Because WireGuard is lightweight and optimized directly inside the Linux kernel, a baseline VPS with 1-2 vCPUs and 1GB-2GB RAM can easily handle personal or small-team encryption tunnels.
Do I get a dedicated IP with a self-hosted VPN?
Yes. When you deploy WireGuard on a VPS, your VPN traffic routes out through your server’s dedicated public IP address.
Take Control of Your Network Privacy Today
Learning how to build your own VPN is the single best decision you can make to guarantee complete digital independence, predictable hosting costs, and unbreakable data security. Don’t leave your confidential traffic in the hands of third-party public networks.
At TezHost, we provide high-speed cloud infrastructure backed by automated one-click installers and 24/7 expert support. Launch your private server today on our high-performance cloud servers, or talk to a sales agent to build a custom solution for your engineering team!